Vue lecture

Il y a de nouveaux articles disponibles, cliquez pour rafraîchir la page.

Passkey lures hide a slow Microsoft 365 data-theft campaign

Passkey lures hide a slow Microsoft 365 data-theft campaign
Microsoft is warning that attackers are using fake passkey and SSO updates to compromise Microsoft 365 identities, then quietly map tenants and collect files and email for hours or days. The campaign, active since May 2026, combines help-desk impersonation, device-code or adversary-in-the-middle phishing, unauthorized MFA enrollment, and automated Microsoft Graph activity.

Source

Entra ID passkeys become default in 2026 as SMS and voice authentication near retirement

Entra ID passkeys become default in 2026 as SMS and voice authentication near retirement
Entra ID administrators have two deadlines to prepare for: passkeys will become the default sign-in method beginning September 1, 2026, and Microsoft-provided SMS and voice authentication will retire on February 1, 2027. Organizations should identify affected users now and move them to phishing-resistant authentication before phone-based sign-ins stop working.

Source

1 in 8 credentials in public MCP files are hardcoded secrets

1 in 8 credentials in public MCP files are hardcoded secrets
Hardcoded MCP credentials are exposing AI coding agents’ connections to GitHub, databases, Slack, Notion, and other services. Hush Security’s analysis of about 82,000 public GitHub configuration files found that 12% of credential slots contained literal secrets, while more than half were difficult for conventional scanners to recognize.

Source

Cisco ISE CVSS 10 zero-day is under active attack

Cisco ISE CVSS 10 zero-day is under active attack
Cisco is urging immediate patching for a CVSS 10.0 authentication-bypass zero-day in Identity Services Engine (ISE) and ISE-PIC after confirming that attackers are exploiting it in the wild. CVE-2026-76460 can let unauthenticated remote attackers reach the web management interface through a vulnerable API, with no workaround available.

Source

Microsoft Entra Private Access offers a phased path beyond VPNs

Microsoft Entra Private Access offers a phased path beyond VPNs
Microsoft is outlining a practical route for replacing traditional VPN access with Microsoft Entra Private Access, using identity, device health, and application-level policies instead of broad network tunnels. The phased approach starts with discovering VPN-dependent resources and ends with incremental decommissioning, helping administrators modernize remote access without disrupting critical applications.

Source

Migrate NTLM to Kerberos: FAQ and tips for Windows admins

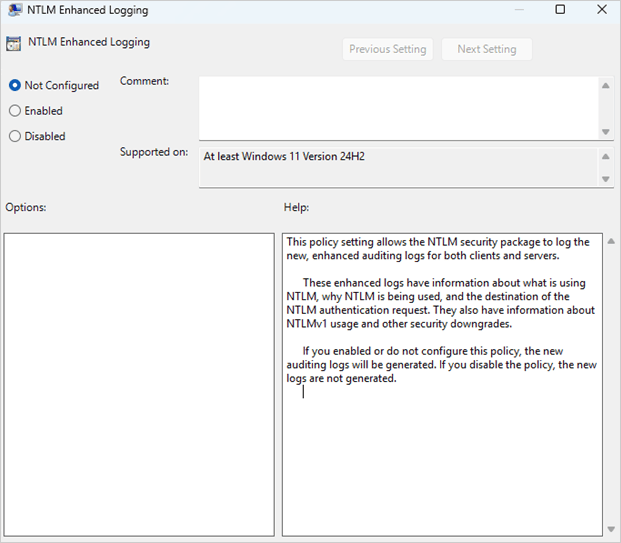
NTLM Enhanced Logging policy (image Microsoft)
Microsoft is retiring NTLM (NT LAN Manager), a legacy challenge-response authentication protocol, in favor of Kerberos, a ticket-based protocol that verifies both the client and the server. NTLM will be disabled by default in the next major Windows Server and client release, but you can start preparing now with enhanced auditing and Kerberos fixes. This article summarizes Microsoft's new FAQ about the upcoming retirement of NTLM.

Source

❌